Telegram Desktop flaw allowed silent file theft through a single link
A bug in Telegram Desktop let attackers steal local files and take over accounts if a user clicked a single link.
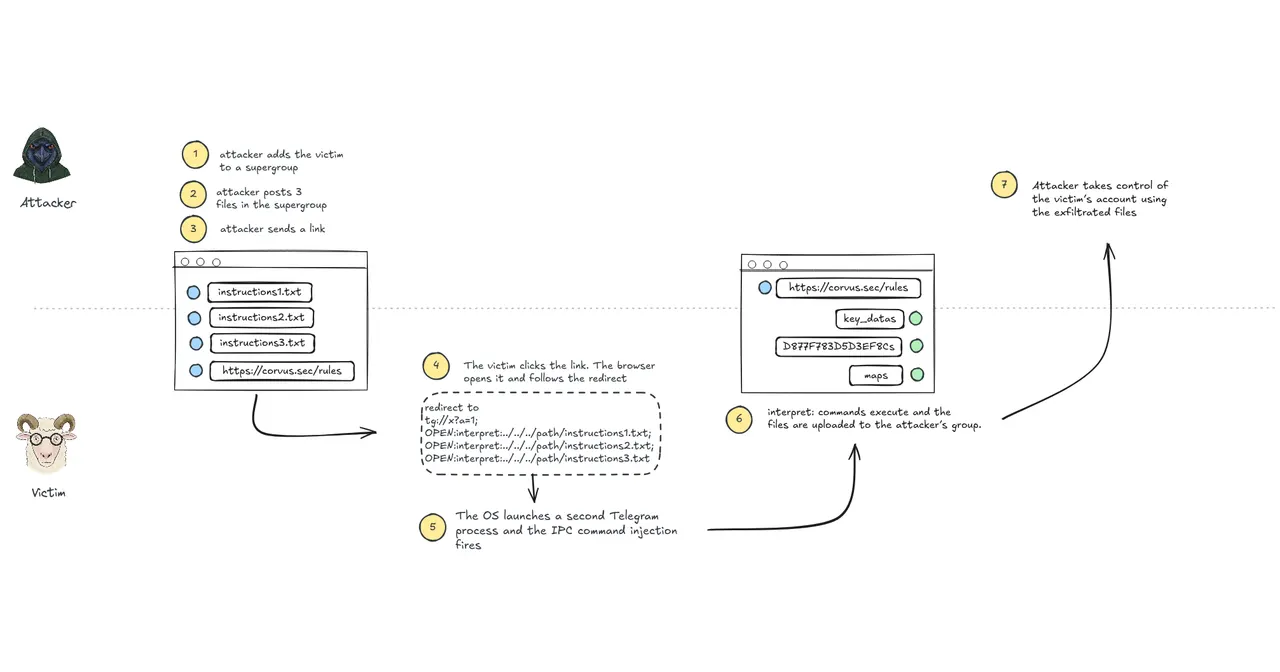
When you click a custom link while Telegram Desktop is already running, a brief helper process flattens the link into text separated by semicolons and passes it to the main app over a local socket. Security researcher BeakSec found that Telegram Desktop through version 7.2.8 failed to escape semicolons in those URLs. That allowed an attacker to inject arbitrary commands, reach an unlisted internal protocol called interpret:, and force Telegram to send local files—including active login sessions—to an attacker-controlled chat without asking for confirmation.
Why it matters: The flaw (CVE-2026-107181, rated 8.1 High) turns a single link click into arbitrary local file exfiltration. By extracting the local files that store your Telegram login state, an attacker gets full account takeover without needing a password or two-factor code.
Know this: Telegram fixed the vulnerability in version 7.2.9 (commit db3405699f). If you use Telegram Desktop on Windows, check your version and update immediately.
The protocol that caused the trouble was originally a internal tool Telegram built to automate posting its own release updates.
Sources
- Telegram Desktop One-Click Account Takeover — https://beaksec.github.io/posts/telegram-desktop-one-click-account-takeover/
- Hacker News Discussion — https://news.ycombinator.com/item?id=50029123